Glossary
Two-Factor Authentication
Two-factor authentication, often shortened to 2FA, uses two different types of proof to check who is signing in. A common example is a password followed by a code from an authenticator app or approval on another device.
Why it matters
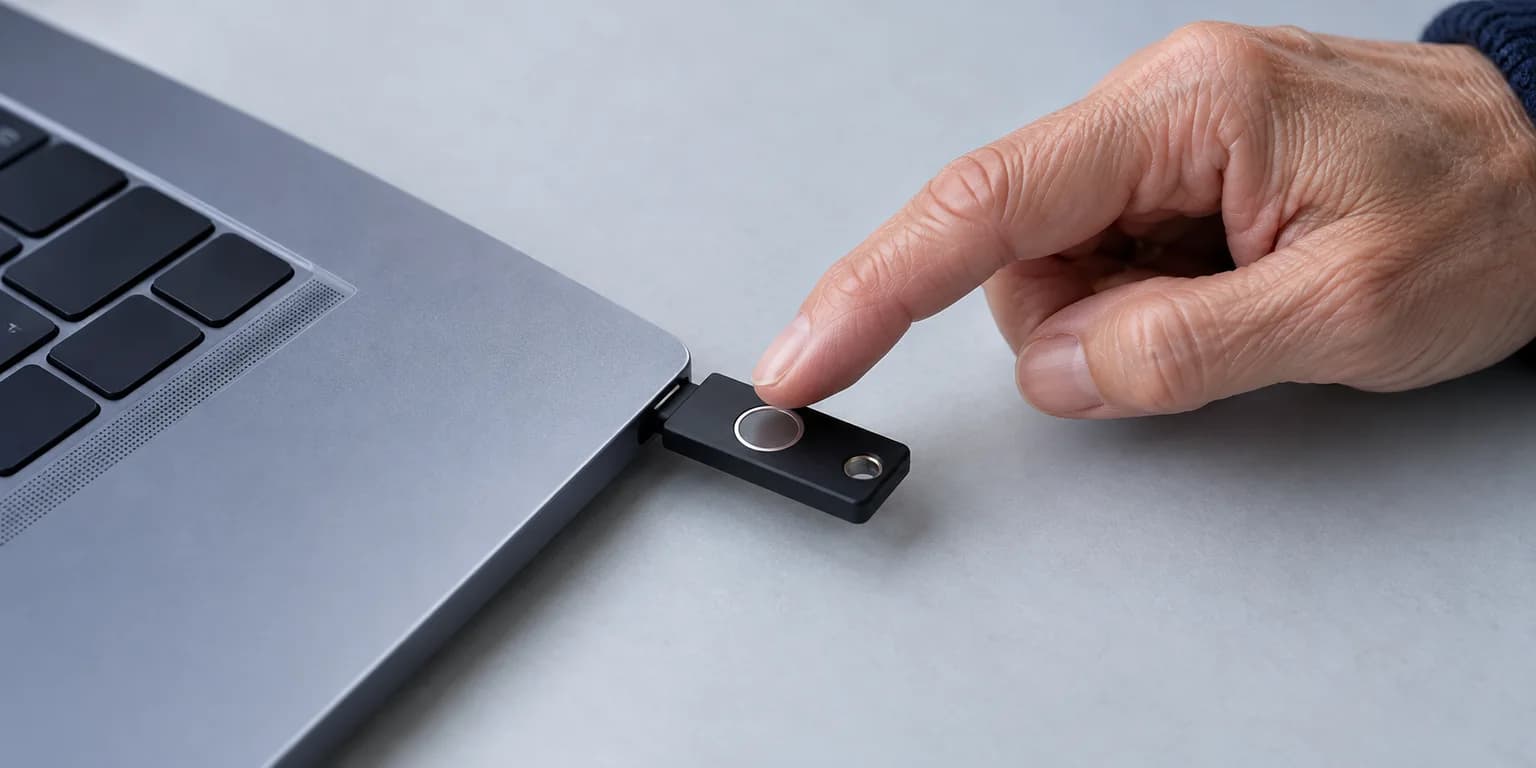
Two-factor authentication protects accounts, but it also explains why a password alone may not allow someone to sign in. The second factor may depend on a phone number, an authenticator app, or a device no one else can unlock. Knowing a password does not give a family member permission to use the account.
Planning for 2FA means documenting how accounts can be recovered, not weakening the security itself.
Common mistakes
- Assuming that a password alone is enough if something happens.
- Canceling mobile service or wiping a device before checking which accounts rely on it for verification.
- Failing to record where authenticator apps, backup codes, or hardware keys are kept.
Safer next steps
- Document which accounts use text codes, authenticator apps, security keys, or approvals on another device.
- Record the location of backup codes and recovery devices in a secure plan.
- Before changing or canceling mobile service, check which accounts use the number and what authorized recovery options are available.